Secure Shipboard LTE Traffic for Maritime Fleets
Secure shipboard LTE traffic with segmented onboard networks, authenticated access, encrypted backhaul, and resilient coverage built for vessels at sea.

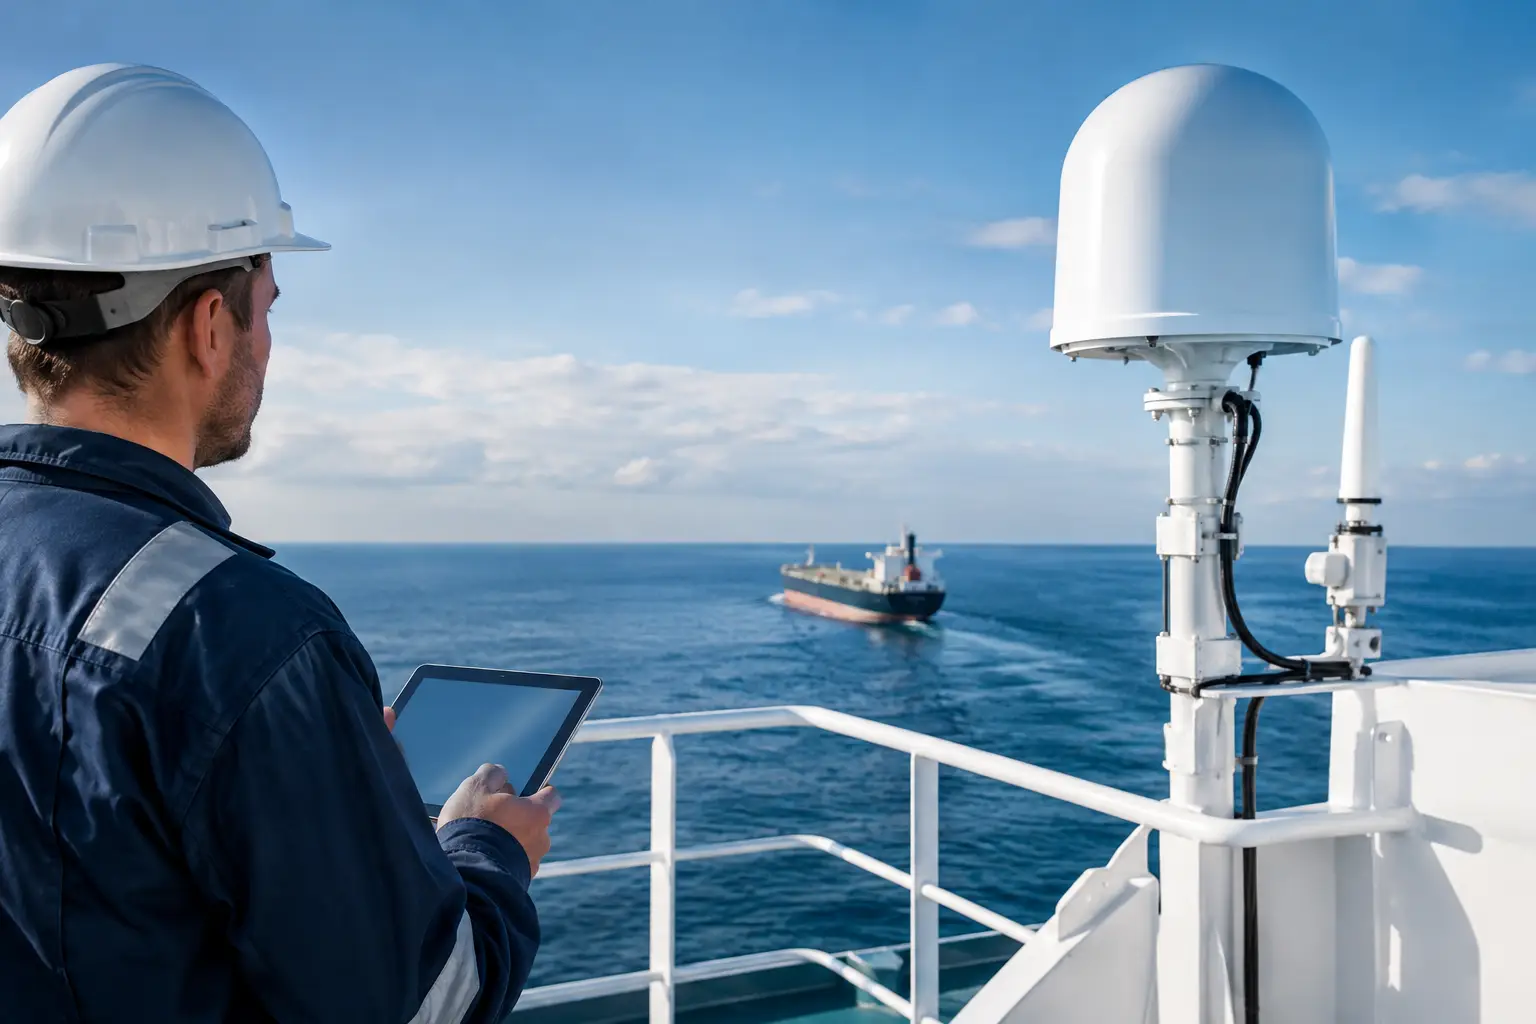
A vessel can have an excellent satellite service, a high-capacity microwave link, and modern onboard Wi-Fi, yet still expose operations if secure shipboard LTE traffic is treated as a basic wireless access problem. It is not. Onboard LTE carries crew devices, operational tablets, machinery telemetry, contractor access, voice services, video, and potentially data moving between the vessel and shore. The network must preserve availability while controlling exactly who can connect, what they can reach, and how traffic leaves the vessel.
For maritime operators, the security model has to account for motion, changing backhaul paths, saltwater exposure, temporary personnel, and long periods without direct IT intervention. That requires engineered radio coverage and a network architecture designed around operational separation, not a single flat onboard LAN.
Why shipboard LTE creates a different security challenge
Private LTE is well suited to ships because SIM-based identity, controlled spectrum, mobility management, and quality-of-service policies provide more control than an unmanaged Wi-Fi environment. But LTE does not automatically make a vessel secure. A poorly designed private LTE deployment can still give an authenticated device unnecessary access to navigation-adjacent systems, industrial controls, or corporate applications.
The risk grows as ships become more connected. A workboat may use LTE for crew communications and broadband access. A larger commercial vessel may add IP cameras, engine-monitoring systems, cargo sensors, maintenance terminals, handheld radios, and remote support applications. Defense and public safety vessels may carry mission networks that require additional isolation and policy control.
These applications do not have the same availability, latency, or security requirements. Crew internet use can tolerate limits during constrained backhaul periods. Machinery alarms and operational voice traffic may not. A network that cannot distinguish between those traffic classes will eventually force an operational compromise.
Secure shipboard LTE traffic starts with network separation
The most effective protection is to establish separation before traffic reaches the backhaul. LTE subscribers should be assigned to distinct logical networks based on their role, device type, and operational purpose. In practical terms, a crew handset should not land in the same security zone as an engineering workstation simply because both are connected to the vessel’s LTE signal.
A well-designed architecture commonly separates four traffic domains:
- Operational technology, including machinery monitoring, sensors, maintenance devices, and approved control-related applications
- Vessel operations, including approved crew communications, work-order systems, internal voice, and operational tablets
- Business and administrative services, including corporate email, approved cloud applications, and managed laptops
- Guest and welfare access, including personal devices and internet use with tightly controlled bandwidth and internet-only policies
Segmentation can be implemented through separate APNs, VLANs, VRFs, firewall zones, dedicated subscriber profiles, or a combination of these controls. The precise approach depends on the private LTE core, onboard routing equipment, and the required integration with shore systems. The principle remains consistent: identity must drive policy, and policy must keep traffic in its proper lane.
This separation also improves fault containment. If a personal device is compromised, the incident should remain within a restricted guest segment rather than becoming a route into operations. If a monitoring device begins generating abnormal traffic, its access can be isolated without disconnecting the entire vessel.
SIM identity is useful only when lifecycle control is enforced
SIM credentials give private LTE a meaningful advantage over open wireless networks, but provisioning discipline matters. Every SIM or eSIM profile needs an accountable owner, an approved device assignment, a defined service profile, and a process for suspension or revocation.
Shared SIMs and undocumented spares create avoidable exposure. So do inactive contractor credentials that remain enabled after a shipyard period or temporary project. Operators should maintain a current inventory that links the subscriber identity to the device, onboard role, permitted network segment, and expected data profile.
For higher-assurance environments, authentication should be reinforced with device controls. A valid SIM in an unauthorized tablet should not automatically receive access to sensitive vessel services. Mobile device management, certificate-based application access, and firewall rules that restrict traffic to known endpoints add useful layers without making the network difficult to operate.
Encrypt the path beyond the vessel
Radio-layer encryption protects traffic over the LTE air interface, but secure shipboard LTE traffic must remain protected as it moves through the onboard network and across the maritime backhaul. The path may shift between stabilized microwave, satellite, cellular, port-based connectivity, or a combination of transport methods. Those changes should not weaken the security model.
An encrypted tunnel between the vessel edge and a shore-side security gateway is the standard operating position for sensitive operational and corporate traffic. The tunnel should use modern cryptography, strong certificate or key management, and monitoring that identifies failures quickly. Where architecture permits, separate tunnels or policy-based routing can keep operational traffic distinct from business and welfare traffic even after it leaves the vessel.
Backhaul redundancy requires careful design. A secondary path is valuable only if failover preserves firewall policy, DNS controls, routing boundaries, and logging. Otherwise, a vessel may maintain connectivity during a primary-link outage while silently bypassing the controls that normally protect it.
Stabilized, auto-aiming microwave systems can provide high-capacity, low-latency connectivity where shore infrastructure and vessel routes support them. Satellite remains essential in many offshore and blue-water operations. The right approach is not to treat one transport as universally better, but to build a policy-driven network that applies the same security controls across each available path.
Control access at the onboard edge
The onboard edge is where radio access, local switching, routing, firewalling, and backhaul policy meet. It must be engineered for the vessel’s real operating environment, including constrained space, intermittent links, vibration, power events, and limited local support.
A security policy should explicitly define which devices can communicate locally, which may reach shore resources, and which are internet-only. Least-privilege access is especially useful for sensors and specialized equipment. A fuel-monitoring gateway, for example, may need to communicate with a defined shore platform and a local maintenance terminal. It does not need broad access to every network reachable from the ship.
Application-aware controls help preserve operational performance. Rate limits, traffic prioritization, and subscriber-level quality of service prevent nonessential downloads, streaming, or software updates from consuming the backhaul needed for voice, alarms, remote diagnostics, or incident coordination. These policies should be tested under degraded-link conditions, not only while the vessel is alongside with abundant bandwidth.
Visibility must continue when shore access is interrupted
A vessel cannot depend entirely on a constant connection to a centralized security operations center. Local logging, alert retention, and configuration backup are essential. When backhaul is available, the vessel should forward security events, subscriber activity, firewall logs, and key network health metrics to shore systems. During an outage, it should retain enough information for later investigation.
Operational teams also need practical alerts. Repeated authentication failures, unexpected data growth, a new device using an operational SIM, traffic to disallowed destinations, or a tunnel failover that changes routing behavior should be visible to the people responsible for the vessel and fleet network.
The goal is not to overwhelm crews with security notifications. It is to give shore-based network teams and authorized vessel personnel actionable evidence when the network behaves outside its approved baseline.
Engineer coverage without creating weak points
Security and RF design are connected. Dead zones cause users to seek workarounds, including unauthorized hotspots, consumer repeaters, or poorly controlled Wi-Fi bridges. Excessive signal spillover around a docked vessel can also increase the opportunity for unwanted connection attempts.
A shipboard LTE design should account for steel bulkheads, deck layouts, machinery spaces, accommodation areas, cargo configurations, and the likely location of operational devices. Antenna placement, power levels, band selection, and sector patterns should deliver the intended service area without broadcasting farther than necessary. Ruggedized components and properly engineered cable paths matter because a degraded RF system often becomes a security problem when personnel improvise around it.
BATS Wireless approaches maritime connectivity as an integrated system of antenna engineering, private LTE design, stabilized communications, and operational support. That system view matters because security policy cannot compensate for unreliable coverage, and high-performance RF cannot compensate for a flat, unmanaged network.
Test the operating model, not just the installation
Commissioning should include more than throughput measurements and coverage surveys. Test whether a crew SIM is blocked from operational assets, whether a contractor profile expires as intended, whether a backhaul failover retains encryption, and whether priority voice traffic stays usable during a heavy data event.
The right test cases reflect how the vessel actually operates: entering port, changing backhaul, conducting maintenance, bringing temporary personnel aboard, operating with reduced bandwidth, or recovering from a power interruption. Periodic reviews are equally necessary because the device inventory, applications, and crew workflows change over the life of the vessel.
Secure maritime LTE is not achieved by adding one appliance at the edge. It is built through identity-based access, deliberate segmentation, encrypted transport, RF coverage engineered for the vessel, and procedures that remain workable when the ship is far from shore. When those elements are designed together, connectivity supports the mission without becoming the mission’s weakest point.
October 26, 2026
October 26, 2026
October 26, 2026
October 26, 2026
